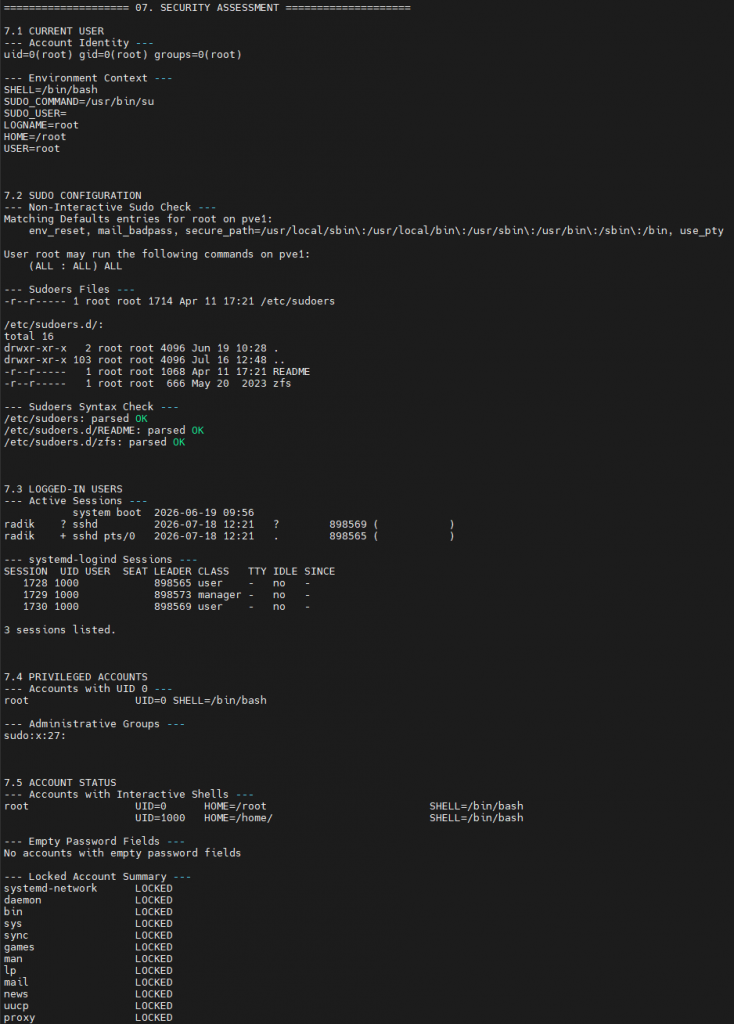
7.1 Current User Context (+ Remote Session Variables)
7.2 Sudo Configuration (+ Visudo Check & Files Listing)
7.3 Logged-in Users & systemd-logind Sessions
7.4 Privileged Accounts (UID 0 & Administrative Groups)
7.5 Account Status (Shells, Empty Passwords & Locked Summary)
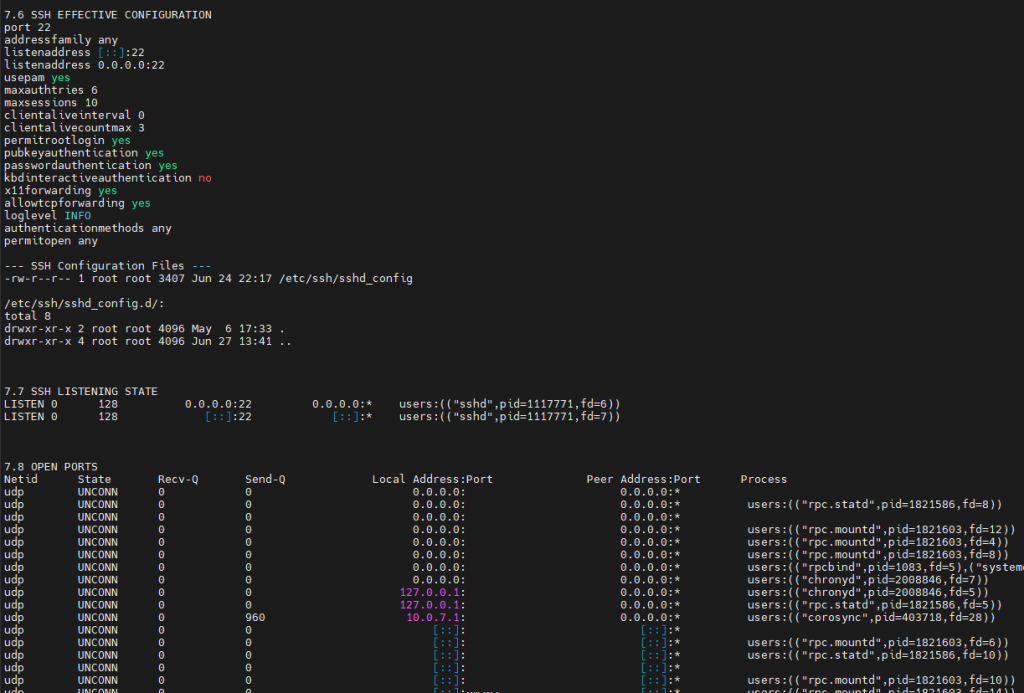
7.6 SSH Effective Configuration (sshd -T Engine Evaluation)
7.7 SSH Listening State7.8 Open Ports (Global Socket Mapping)
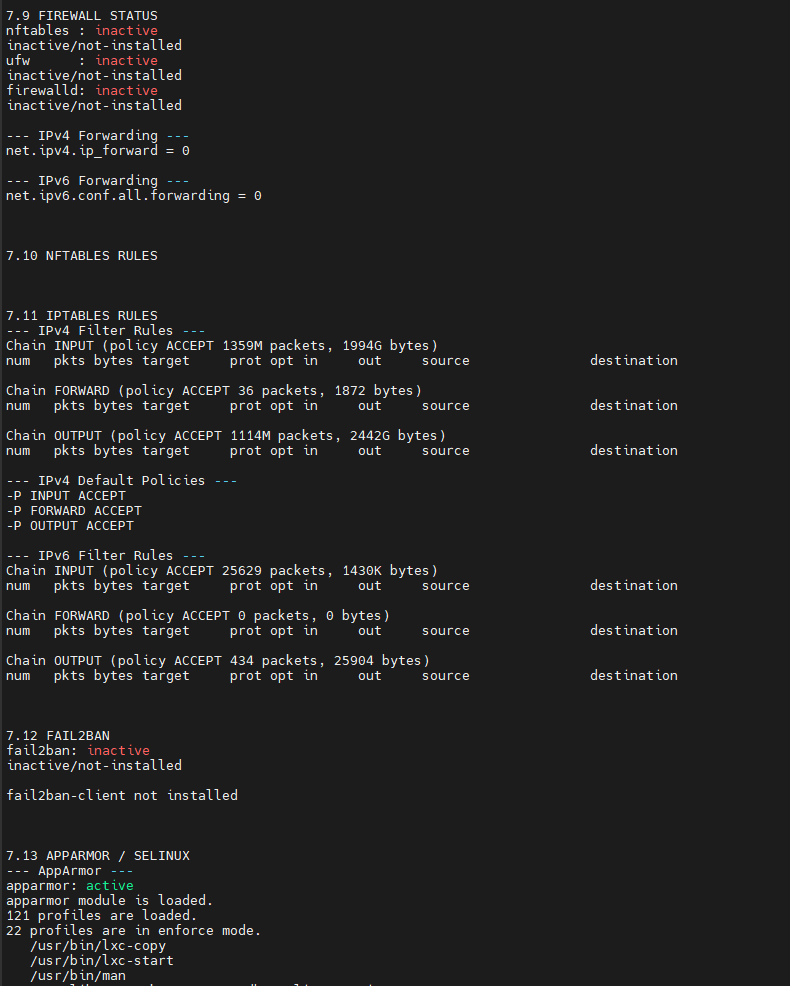
7.9 Firewall Status (+ IPv4/IPv6 Kernel Forwarding States)
7.10 nftables Active Ruleset (Top 120 lines)
7.11 iptables Ruleset (IPv4 & IPv6 Legacy Rule Matrices)
7.12 Fail2ban (Dynamic Active Jails Evaluation Loop)
7.13 AppArmor / SELinux Active Enforcement Profiles
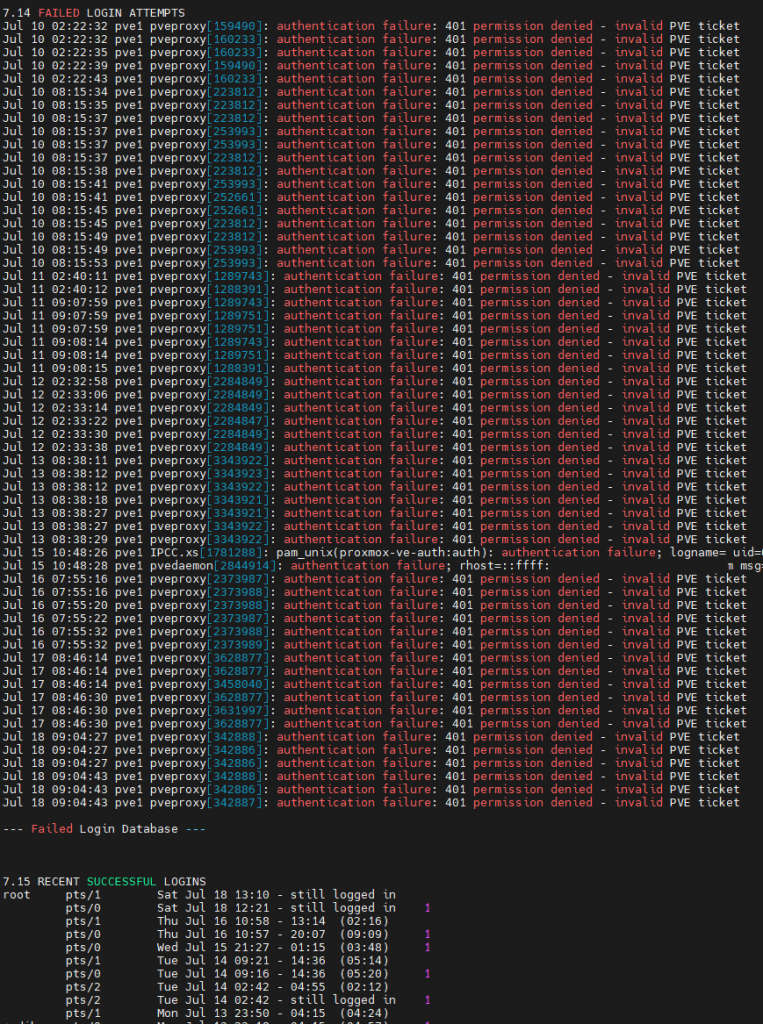
7.14 Failed Login Attempts (Log Grep & lastb DB Hunt)
7.15 Recent Successful Logins (last History Profile)
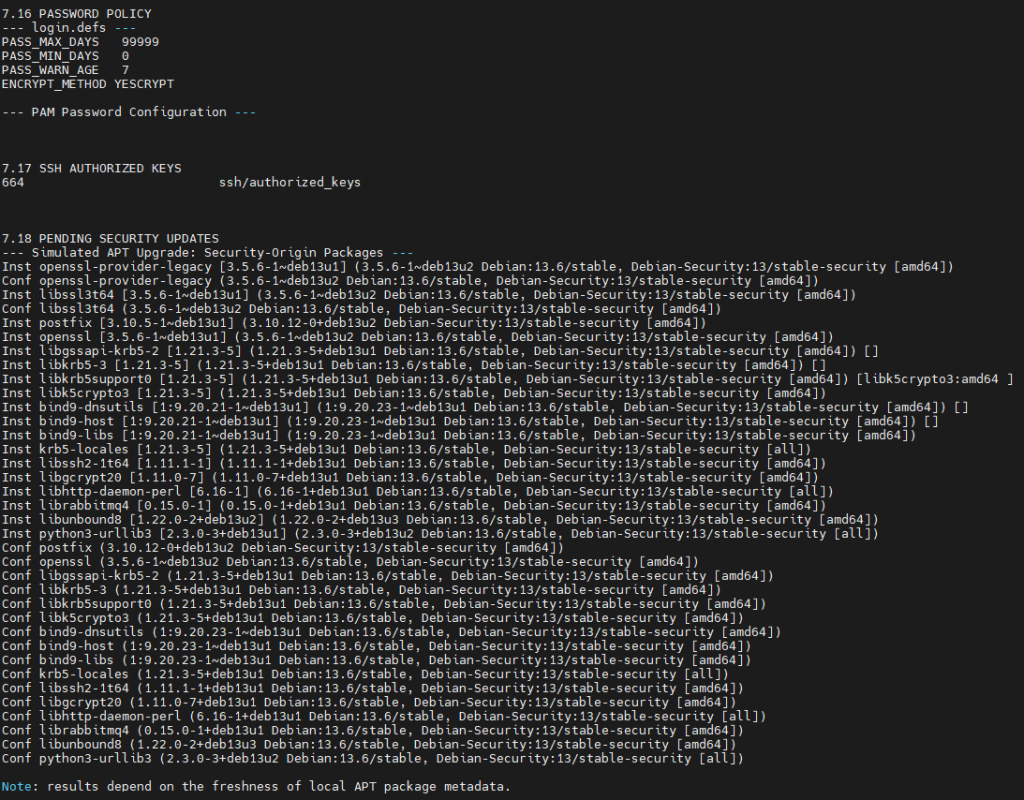
7.16 Password Policy (login.defs Aging & PAM Complexity Vectors)
7.17 SSH Authorized Keys (Permissions & Paths Hunt)
7.18 Pending Security Updates (APT / DNF Metadata Mapping)
Copy–>Past
echo "==================== 07. SECURITY ASSESSMENT ===================="; printf "\n"; echo "7.1 CURRENT USER"; echo "--- Account Identity ---"; id 2>/dev/null || echo "Unable to determine current identity"; printf "\n"; echo "--- Environment Context ---"; env | grep -E '^(USER|LOGNAME|HOME|SHELL|SUDO_USER|SUDO_COMMAND|SSH_CONNECTION|SSH_CLIENT|SSH_TTY)=' || echo "No relevant session variables found"; printf "\n%.0s" {1..3}; echo "7.2 SUDO CONFIGURATION"; echo "--- Non-Interactive Sudo Check ---"; if command -v sudo >/dev/null 2>&1; then timeout 3 sudo -n -l 2>/dev/null || echo "Passwordless sudo unavailable, credentials required, or sudo access denied"; else echo "sudo not installed"; fi; printf "\n"; echo "--- Sudoers Files ---"; ls -la /etc/sudoers /etc/sudoers.d/ 2>/dev/null || echo "Sudoers configuration unavailable or access restricted"; printf "\n"; echo "--- Sudoers Syntax Check ---"; if command -v visudo >/dev/null 2>&1; then timeout 5 sudo -n visudo -c 2>/dev/null || echo "Unable to validate sudoers without elevated privileges"; else echo "visudo not installed"; fi; printf "\n%.0s" {1..3}; echo "7.3 LOGGED-IN USERS"; echo "--- Active Sessions ---"; who -a 2>/dev/null || w 2>/dev/null || echo "Unable to inspect active sessions"; printf "\n"; echo "--- systemd-logind Sessions ---"; loginctl list-sessions --no-pager 2>/dev/null || echo "systemd-logind session data unavailable"; printf "\n%.0s" {1..3}; echo "7.4 PRIVILEGED ACCOUNTS"; echo "--- Accounts with UID 0 ---"; awk -F: '$3 == 0 {printf "%-20s UID=%s SHELL=%s\n", $1, $3, $7}' /etc/passwd 2>/dev/null || echo "Unable to inspect /etc/passwd"; printf "\n"; echo "--- Administrative Groups ---"; getent group sudo 2>/dev/null || echo "sudo group not found"; getent group admin 2>/dev/null || true; getent group wheel 2>/dev/null || true; printf "\n%.0s" {1..3}; echo "7.5 ACCOUNT STATUS"; echo "--- Accounts with Interactive Shells ---"; awk -F: '$7 !~ /(nologin|false|sync)$/ { printf "%-20s UID=%-6s HOME=%-30s SHELL=%s\n", $1, $3, $6, $7 }' /etc/passwd 2>/dev/null || echo "Unable to inspect account shells"; printf "\n"; echo "--- Empty Password Fields ---"; if [ -r /etc/shadow ]; then awk -F: '$2 == "" {print $1}' /etc/shadow; EMPTY_PASSWORD_COUNT=$(awk -F: '$2 == "" {count++} END {print count+0}' /etc/shadow); [ "${EMPTY_PASSWORD_COUNT:-0}" -eq 0 ] && echo "No accounts with empty password fields"; else echo "/etc/shadow requires elevated privileges"; fi; printf "\n"; echo "--- Locked Account Summary ---"; if [ -r /etc/shadow ]; then awk -F: '$2 ~ /^(!|\*)/ { printf "%-20s LOCKED\n", $1 }' /etc/shadow | head -40; else echo "/etc/shadow requires elevated privileges"; fi; printf "\n%.0s" {1..3}; echo "7.6 SSH EFFECTIVE CONFIGURATION"; if command -v sshd >/dev/null 2>&1; then sshd -T 2>/dev/null | grep -E '^(port|listenaddress|addressfamily|permitrootlogin|passwordauthentication|kbdinteractiveauthentication|pubkeyauthentication|authenticationmethods|maxauthtries|maxsessions|allowusers|allowgroups|denyusers|denygroups|x11forwarding|allowtcpforwarding|permitopen|clientaliveinterval|clientalivecountmax|loglevel|usepam) ' || echo "Unable to read effective sshd configuration"; else echo "sshd not installed"; fi; printf "\n"; echo "--- SSH Configuration Files ---"; ls -la /etc/ssh/sshd_config /etc/ssh/sshd_config.d/ 2>/dev/null || echo "SSH server configuration files unavailable"; printf "\n%.0s" {1..3}; echo "7.7 SSH LISTENING STATE"; ss -ltnp 2>/dev/null | grep -Ei 'sshd|ssh' || echo "No active SSH listener associated with sshd"; printf "\n%.0s" {1..3}; echo "7.8 OPEN PORTS"; ss -tulpn 2>/dev/null || echo "Socket information unavailable"; printf "\n%.0s" {1..3}; echo "7.9 FIREWALL STATUS"; echo "nftables : $(systemctl is-active nftables 2>/dev/null || echo inactive/not-installed)"; echo "ufw : $(systemctl is-active ufw 2>/dev/null || echo inactive/not-installed)"; echo "firewalld: $(systemctl is-active firewalld 2>/dev/null || echo inactive/not-installed)"; printf "\n"; echo "--- IPv4 Forwarding ---"; sysctl net.ipv4.ip_forward 2>/dev/null || echo "IPv4 forwarding status unavailable"; printf "\n"; echo "--- IPv6 Forwarding ---"; sysctl net.ipv6.conf.all.forwarding 2>/dev/null || echo "IPv6 forwarding status unavailable"; printf "\n%.0s" {1..3}; echo "7.10 NFTABLES RULES"; if command -v nft >/dev/null 2>&1; then nft list ruleset 2>/dev/null | head -120 || echo "nftables rules unavailable or insufficient privileges"; else echo "nft command not installed"; fi; printf "\n%.0s" {1..3}; echo "7.11 IPTABLES RULES"; if command -v iptables >/dev/null 2>&1; then echo "--- IPv4 Filter Rules ---"; iptables -L -n -v --line-numbers 2>/dev/null | head -120 || echo "IPv4 iptables rules unavailable"; printf "\n"; echo "--- IPv4 Default Policies ---" ; iptables -S 2>/dev/null | grep '^-P ' || echo "IPv4 default policies unavailable"; else echo "iptables not installed"; fi; printf "\n"; if command -v ip6tables >/dev/null 2>&1; then echo "--- IPv6 Filter Rules ---"; ip6tables -L -n -v --line-numbers 2>/dev/null | head -80 || echo "IPv6 iptables rules unavailable"; fi; printf "\n%.0s" {1..3}; echo "7.12 FAIL2BAN"; echo "fail2ban: $(systemctl is-active fail2ban 2>/dev/null || echo inactive/not-installed)"; printf "\n"; if command -v fail2ban-client >/dev/null 2>&1; then fail2ban-client status 2>/dev/null || echo "Unable to query fail2ban status"; printf "\n"; JAILS=$(fail2ban-client status 2>/dev/null | awk -F: '/Jail list/ { gsub(/[ \t]/, "", $2); print $2 }'); if [ -n "$JAILS" ]; then OLD_IFS=$IFS; IFS=','; for JAIL in $JAILS; do echo "--- Jail: $JAIL ---"; fail2ban-client status "$JAIL" 2>/dev/null | head -30; printf "\n"; done; IFS=$OLD_IFS; fi; else echo "fail2ban-client not installed"; fi; printf "\n%.0s" {1..3}; echo "7.13 APPARMOR / SELINUX"; echo "--- AppArmor ---"; echo "apparmor: $(systemctl is-active apparmor 2>/dev/null || echo inactive/not-installed)"; if command -v aa-status >/dev/null 2>&1; then aa-status 2>/dev/null | head -40 || echo "Unable to query AppArmor status"; elif [ -f /sys/kernel/security/apparmor/profiles ]; then echo "AppArmor kernel interface detected"; else echo "AppArmor not detected"; fi; printf "\n"; echo "--- SELinux ---"; if command -v sestatus >/dev/null 2>&1; then sestatus 2>/dev/null; else echo "SELinux tools not installed"; fi; printf "\n%.0s" {1..3}; echo "7.14 FAILED LOGIN ATTEMPTS"; if command -v journalctl >/dev/null 2>&1; then journalctl -b 0 --no-pager 2>/dev/null | grep -Ei 'failed password|invalid user|authentication failure|pam_unix.*authentication failure|maximum authentication attempts exceeded|connection closed by authenticating user' | tail -60 || echo "No failed login attempts found in current boot"; else grep -Eih 'failed password|invalid user|authentication failure|maximum authentication attempts exceeded' /var/log/auth.log /var/log/secure 2>/dev/null | tail -60 || echo "Authentication logs unavailable"; fi; printf "\n"; echo "--- Failed Login Database ---"; lastb 2>/dev/null | head -30 || echo "Failed login database unavailable or access restricted"; printf "\n%.0s" {1..3}; echo "7.15 RECENT SUCCESSFUL LOGINS"; last -a 2>/dev/null | head -30 || echo "Login history unavailable"; printf "\n%.0s" {1..3}; echo "7.16 PASSWORD POLICY"; echo "--- login.defs ---"; grep -E '^[[:space:]]*(PASS_MAX_DAYS|PASS_MIN_DAYS|PASS_WARN_AGE|PASS_MIN_LEN|ENCRYPT_METHOD|UMASK)[[:space:]]+' /etc/login.defs 2>/dev/null || echo "Password aging settings unavailable"; printf "\n"; echo "--- PAM Password Configuration ---"; grep -R -E 'pam_pwquality|pam_cracklib|pam_pwhistory|remember=|minlen=|retry=' /etc/pam.d/ /etc/security/pwquality.conf /etc/security/pwquality.conf.d/ 2>/dev/null | head -60 || echo "No explicit PAM password-quality settings found"; printf "\n%.0s" {1..3}; echo "7.17 SSH AUTHORIZED KEYS"; find /root /home -xdev -type f -path '*/.ssh/authorized_keys' -printf '%m %u:%g %p\n' 2>/dev/null || echo "No authorized_keys files found or access restricted"; printf "\n%.0s" {1..3}; echo "7.18 PENDING SECURITY UPDATES"; if command -v apt-get >/dev/null 2>&1; then echo "--- Simulated APT Upgrade: Security-Origin Packages ---"; apt-get -s upgrade 2>/dev/null | grep -Ei 'Inst .*security|Debian-Security|Ubuntu.*security' | head -80 || echo "No security-origin package upgrades detected in current APT metadata"; printf "\n"; echo "Note: results depend on the freshness of local APT package metadata."; elif command -v dnf >/dev/null 2>&1; then echo "--- DNF Security Updates ---"; dnf updateinfo list security 2>/dev/null | head -80 || echo "No security advisories detected in current DNF metadata"; else echo "Supported package manager not found"; fi
# ==================== 07. SECURITY ASSESSMENT ====================
echo "==================== 07. SECURITY ASSESSMENT ===================="
printf "\n"

# --- 7.1 CURRENT USER ---
echo "7.1 CURRENT USER"
echo "--- Account Identity ---"
id 2>/dev/null || echo "Unable to determine current identity"
printf "\n"
echo "--- Environment Context ---"
env | grep -E '^(USER|LOGNAME|HOME|SHELL|SUDO_USER|SUDO_COMMAND|SSH_CONNECTION|SSH_CLIENT|SSH_TTY)=' || echo "No relevant session variables found"
printf "\n%.0s" {1..3}

# --- 7.2 SUDO CONFIGURATION ---
echo "7.2 SUDO CONFIGURATION"
echo "--- Non-Interactive Sudo Check ---"
if command -v sudo >/dev/null 2>&1; then
    timeout 3 sudo -n -l 2>/dev/null || echo "Passwordless sudo unavailable, credentials required, or sudo access denied"
else
    echo "sudo not installed"
fi
printf "\n"
echo "--- Sudoers Files ---"
ls -la /etc/sudoers /etc/sudoers.d/ 2>/dev/null || echo "Sudoers configuration unavailable or access restricted"
printf "\n"
echo "--- Sudoers Syntax Check ---"
if command -v visudo >/dev/null 2>&1; then
    timeout 5 sudo -n visudo -c 2>/dev/null || echo "Unable to validate sudoers without elevated privileges"
else
    echo "visudo not installed"
fi
printf "\n%.0s" {1..3}

# --- 7.3 LOGGED-IN USERS ---
echo "7.3 LOGGED-IN USERS"
echo "--- Active Sessions ---"
who -a 2>/dev/null || w 2>/dev/null || echo "Unable to inspect active sessions"
printf "\n"
echo "--- systemd-logind Sessions ---"
loginctl list-sessions --no-pager 2>/dev/null || echo "systemd-logind session data unavailable"
printf "\n%.0s" {1..3}

# --- 7.4 PRIVILEGED ACCOUNTS ---
echo "7.4 PRIVILEGED ACCOUNTS"
echo "--- Accounts with UID 0 ---"
awk -F: '$3 == 0 {printf "%-20s UID=%s SHELL=%s\n", $1, $3, $7}' /etc/passwd 2>/dev/null || echo "Unable to inspect /etc/passwd"
printf "\n"
echo "--- Administrative Groups ---"
getent group sudo 2>/dev/null || echo "sudo group not found"
getent group admin 2>/dev/null || true
getent group wheel 2>/dev/null || true
printf "\n%.0s" {1..3}

# --- 7.5 ACCOUNT STATUS ---
echo "7.5 ACCOUNT STATUS"
echo "--- Accounts with Interactive Shells ---"
awk -F: '$7 !~ /(nologin|false|sync)$/ { printf "%-20s UID=%-6s HOME=%-30s SHELL=%s\n", $1, $3, $6, $7 }' /etc/passwd 2>/dev/null || echo "Unable to inspect account shells"
printf "\n"
echo "--- Empty Password Fields ---"
if [ -r /etc/shadow ]; then
    awk -F: '$2 == "" {print $1}' /etc/shadow
    EMPTY_PASSWORD_COUNT=$(awk -F: '$2 == "" {count++} END {print count+0}' /etc/shadow)
    [ "${EMPTY_PASSWORD_COUNT:-0}" -eq 0 ] && echo "No accounts with empty password fields"
else
    echo "/etc/shadow requires elevated privileges"
fi
printf "\n"
echo "--- Locked Account Summary ---"
if [ -r /etc/shadow ]; then
    awk -F: '$2 ~ /^(!|\*)/ { printf "%-20s LOCKED\n", $1 }' /etc/shadow | head -40
else
    echo "/etc/shadow requires elevated privileges"
fi
printf "\n%.0s" {1..3}

# --- 7.6 SSH EFFECTIVE CONFIGURATION ---
echo "7.6 SSH EFFECTIVE CONFIGURATION"
if command -v sshd >/dev/null 2>&1; then
    sshd -T 2>/dev/null | grep -E '^(port|listenaddress|addressfamily|permitrootlogin|passwordauthentication|kbdinteractiveauthentication|pubkeyauthentication|authenticationmethods|maxauthtries|maxsessions|allowusers|allowgroups|denyusers|denygroups|x11forwarding|allowtcpforwarding|permitopen|clientaliveinterval|clientalivecountmax|loglevel|usepam) ' || echo "Unable to read effective sshd configuration"
else
    echo "sshd not installed"
fi
printf "\n"
echo "--- SSH Configuration Files ---"
ls -la /etc/ssh/sshd_config /etc/ssh/sshd_config.d/ 2>/dev/null || echo "SSH server configuration files unavailable"
printf "\n%.0s" {1..3}

# --- 7.7 SSH LISTENING STATE ---
echo "7.7 SSH LISTENING STATE"
ss -ltnp 2>/dev/null | grep -Ei 'sshd|ssh' || echo "No active SSH listener associated with sshd"
printf "\n%.0s" {1..3}

# --- 7.8 OPEN PORTS ---
echo "7.8 OPEN PORTS"
ss -tulpn 2>/dev/null || echo "Socket information unavailable"
printf "\n%.0s" {1..3}

# --- 7.9 FIREWALL STATUS ---
echo "7.9 FIREWALL STATUS"
echo "nftables : $(systemctl is-active nftables 2>/dev/null || echo inactive/not-installed)"
echo "ufw      : $(systemctl is-active ufw 2>/dev/null || echo inactive/not-installed)"
echo "firewalld: $(systemctl is-active firewalld 2>/dev/null || echo inactive/not-installed)"
printf "\n"
echo "--- IPv4 Forwarding ---"
sysctl net.ipv4.ip_forward 2>/dev/null || echo "IPv4 forwarding status unavailable"
printf "\n"
echo "--- IPv6 Forwarding ---"
sysctl net.ipv6.conf.all.forwarding 2>/dev/null || echo "IPv6 forwarding status unavailable"
printf "\n%.0s" {1..3}

# --- 7.10 NFTABLES RULES ---
echo "7.10 NFTABLES RULES"
if command -v nft >/dev/null 2>&1; then
    nft list ruleset 2>/dev/null | head -120 || echo "nftables rules unavailable or insufficient privileges"
else
    echo "nft command not installed"
fi
printf "\n%.0s" {1..3}

# --- 7.11 IPTABLES RULES ---
echo "7.11 IPTABLES RULES"
if command -v iptables >/dev/null 2>&1; then
    echo "--- IPv4 Filter Rules ---"
    iptables -L -n -v --line-numbers 2>/dev/null | head -120 || echo "IPv4 iptables rules unavailable"
    printf "\n"
    echo "--- IPv4 Default Policies ---"
    iptables -S 2>/dev/null | grep '^-P ' || echo "IPv4 default policies unavailable"
else
    echo "iptables not installed"
fi
printf "\n"
if command -v ip6tables >/dev/null 2>&1; then
    echo "--- IPv6 Filter Rules ---"
    ip6tables -L -n -v --line-numbers 2>/dev/null | head -80 || echo "IPv6 iptables rules unavailable"
fi
printf "\n%.0s" {1..3}

# --- 7.12 FAIL2BAN ---
echo "7.12 FAIL2BAN"
echo "fail2ban: $(systemctl is-active fail2ban 2>/dev/null || echo inactive/not-installed)"
printf "\n"
if command -v fail2ban-client >/dev/null 2>&1; then
    fail2ban-client status 2>/dev/null || echo "Unable to query fail2ban status"
    printf "\n"
    JAILS=$(fail2ban-client status 2>/dev/null | awk -F: '/Jail list/ { gsub(/[ \t]/, "", $2); print $2 }')
    if [ -n "$JAILS" ]; then
        OLD_IFS=$IFS
        IFS=','
        for JAIL in $JAILS; do
            echo "--- Jail: $JAIL ---"
            fail2ban-client status "$JAIL" 2>/dev/null | head -30
            printf "\n"
        done
        IFS=$OLD_IFS
    fi
else
    echo "fail2ban-client not installed"
fi
printf "\n%.0s" {1..3}

# --- 7.13 APPARMOR / SELINUX ---
echo "7.13 APPARMOR / SELINUX"
echo "--- AppArmor ---"
echo "apparmor: $(systemctl is-active apparmor 2>/dev/null || echo inactive/not-installed)"
if command -v aa-status >/dev/null 2>&1; then
    aa-status 2>/dev/null | head -40 || echo "Unable to query AppArmor status"
elif [ -f /sys/kernel/security/apparmor/profiles ]; then
    echo "AppArmor kernel interface detected"
else
    echo "AppArmor not detected"
fi
printf "\n"
echo "--- SELinux ---"
if command -v sestatus >/dev/null 2>&1; then
    sestatus 2>/dev/null
else
    echo "SELinux tools not installed"
fi
printf "\n%.0s" {1..3}

# --- 7.14 FAILED LOGIN ATTEMPTS ---
echo "7.14 FAILED LOGIN ATTEMPTS"
if command -v journalctl >/dev/null 2>&1; then
    journalctl -b 0 --no-pager 2>/dev/null | grep -Ei 'failed password|invalid user|authentication failure|pam_unix.*authentication failure|maximum authentication attempts exceeded|connection closed by authenticating user' | tail -60 || echo "No failed login attempts found in current boot"
else
    grep -Eih 'failed password|invalid user|authentication failure|maximum authentication attempts exceeded' /var/log/auth.log /var/log/secure 2>/dev/null | tail -60 || echo "Authentication logs unavailable"
fi
printf "\n"
echo "--- Failed Login Database ---"
lastb 2>/dev/null | head -30 || echo "Failed login database unavailable or access restricted"
printf "\n%.0s" {1..3}

# --- 7.15 RECENT SUCCESSFUL LOGINS ---
echo "7.15 RECENT SUCCESSFUL LOGINS"
last -a 2>/dev/null | head -30 || echo "Login history unavailable"
printf "\n%.0s" {1..3}

# --- 7.16 PASSWORD POLICY ---
echo "7.16 PASSWORD POLICY"
echo "--- login.defs ---"
grep -E '^[[:space:]]*(PASS_MAX_DAYS|PASS_MIN_DAYS|PASS_WARN_AGE|PASS_MIN_LEN|ENCRYPT_METHOD|UMASK)[[:space:]]+' /etc/login.defs 2>/dev/null || echo "Password aging settings unavailable"
printf "\n"
echo "--- PAM Password Configuration ---"
grep -R -E 'pam_pwquality|pam_cracklib|pam_pwhistory|remember=|minlen=|retry=' /etc/pam.d/ /etc/security/pwquality.conf /etc/security/pwquality.conf.d/ 2>/dev/null | head -60 || echo "No explicit PAM password-quality settings found"
printf "\n%.0s" {1..3}

# --- 7.17 SSH AUTHORIZED KEYS ---
echo "7.17 SSH AUTHORIZED KEYS"
find /root /home -xdev -type f -path '*/.ssh/authorized_keys' -printf '%m %u:%g %p\n' 2>/dev/null || echo "No authorized_keys files found or access restricted"
printf "\n%.0s" {1..3}

# --- 7.18 PENDING SECURITY UPDATES ---
echo "7.18 PENDING SECURITY UPDATES"
if command -v apt-get >/dev/null 2>&1; then
    echo "--- Simulated APT Upgrade: Security-Origin Packages ---"
    apt-get -s upgrade 2>/dev/null | grep -Ei 'Inst .*security|Debian-Security|Ubuntu.*security' | head -80 || echo "No security-origin package upgrades detected in current APT metadata"
    printf "\n"
    echo "Note: results depend on the freshness of local APT package metadata."
elif command -v dnf >/dev/null 2>&1; then
    echo "--- DNF Security Updates ---"
    dnf updateinfo list security 2>/dev/null | head -80 || echo "No security advisories detected in current DNF metadata"
else
    echo "Supported package manager not found"
fi